9 seconds to wipe production
A Cursor agent running Claude Opus 4.6 used an over-scoped Railway token to delete PocketOS's production database and volume-level backups in a single API call.
We help teams make AI agents safer to run in production by identifying where they can be abused, putting the right safeguards in place, and validating them through hands-on security testing.
A Cursor agent running Claude Opus 4.6 used an over-scoped Railway token to delete PocketOS's production database and volume-level backups in a single API call.
Replit acknowledged an incident where its Agent deleted customer data because development activity could affect the production database. Replit then introduced default development and production database isolation.
Agents make dynamic tool decisions, process untrusted content and can operate with machine credentials. A compromised or manipulated agent can become an execution path into the systems it can reach.
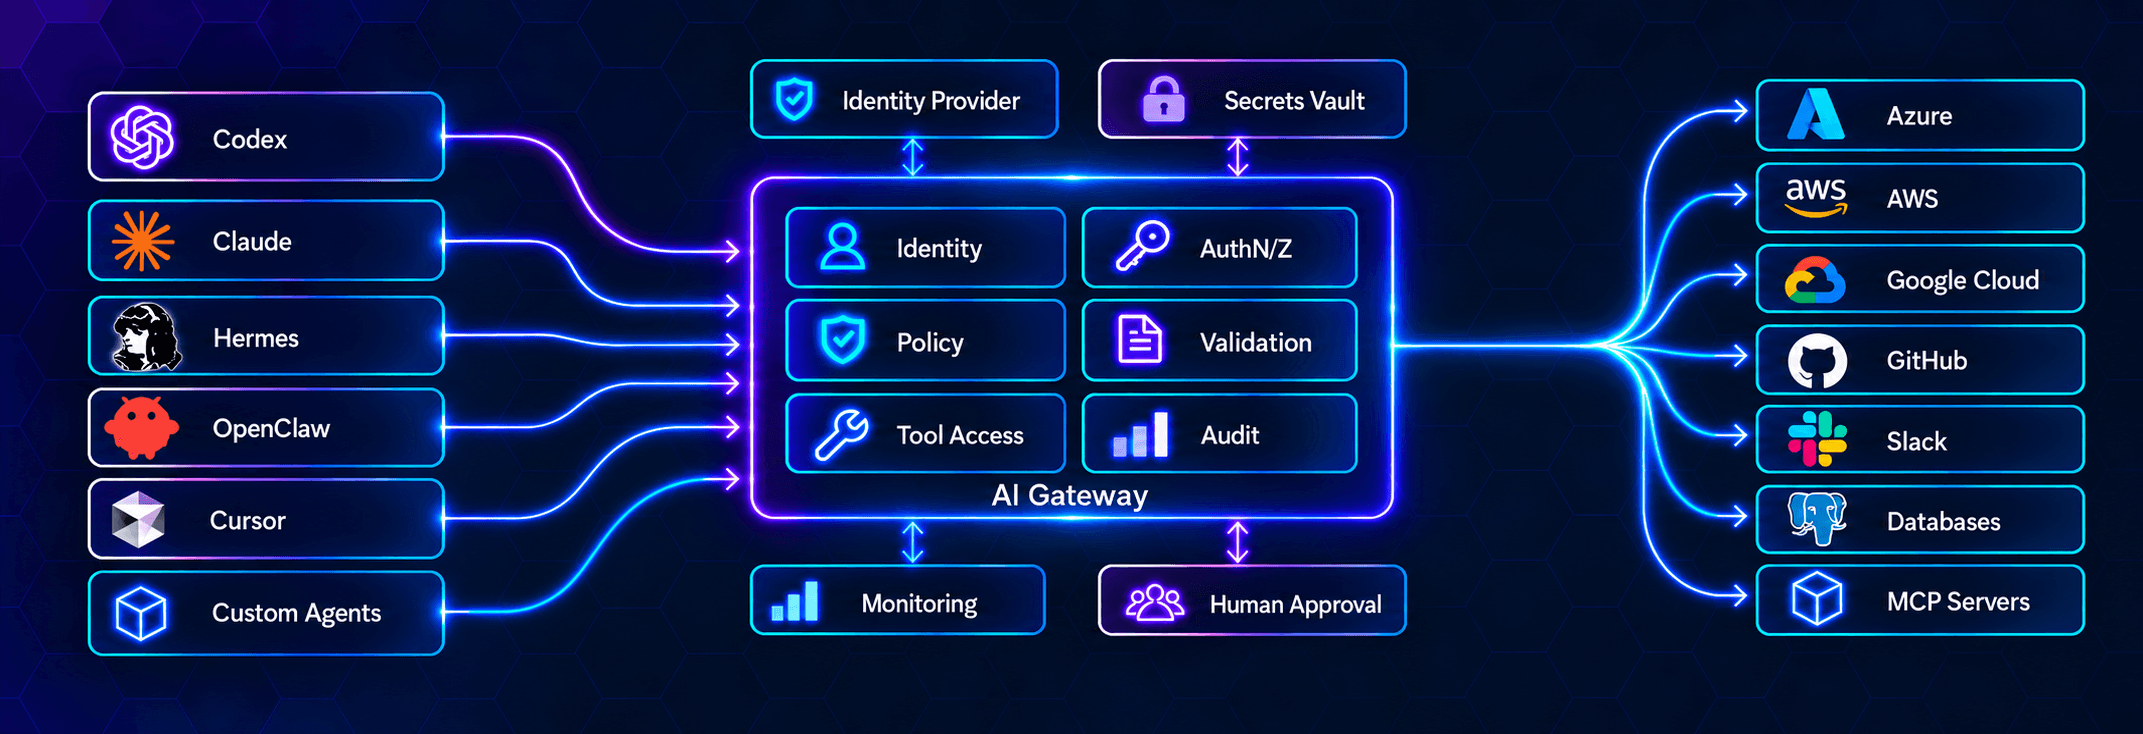
AI agent security is the practice of protecting AI agents, the identities and credentials they use, the tools they can invoke, and the systems they can access. It includes agent authentication and authorization, least-privilege access, MCP and tool security, secrets management, runtime policy enforcement, human approval for sensitive actions, agent-to-agent security, and audit logging. The goal is to keep agentic AI systems within defined security and execution boundaries even when an agent makes an incorrect decision or processes malicious content.
Get a focused review of your AI agent, MCP and tool-access architecture — and a prioritized plan for centralized security controls.