Pass Your SOC 2 Audit with Confidence
Hands-on consulting for SaaS teams preparing for SOC 2 and other audit standards. We help you assess readiness, implement controls and maintain evidence as your business grows.
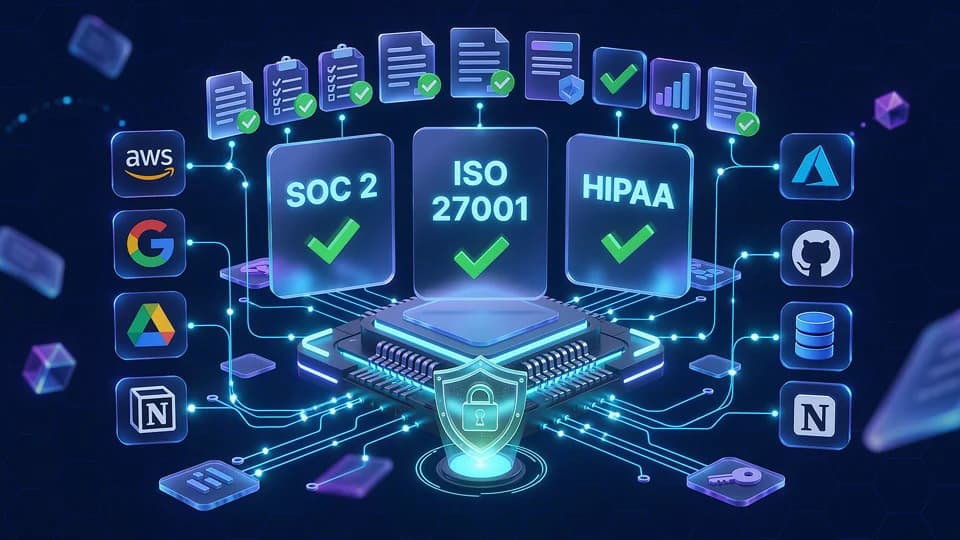
From your first assessment to everyday compliance
Start with a clear view of readiness. Get practical help implementing controls, then keep them working with ongoing support.
Compliance partners
We connect the capabilities of your compliance platform with the policies, controls and evidence your team needs to own.




Ready for Type I. Build toward Type II.
Type I establishes a point-in-time view of control design. Type II examines how effectively those controls operate over an observation period. We help you make that next step part of the same journey.
Turn implemented controls into consistent practice
We help establish recurring activities, coordinate control owners, collect evidence across the observation period and resolve gaps before the independent examination.
- Recurring control activities and ownership
- Evidence that demonstrates operation over time
- Preparation and support for auditor requests
A clearer view of your SOC 2 journey
Type I evaluates the design of controls at a specific point in time. Type II also evaluates how effectively those controls operate over a defined observation period. We help you prepare for Type I and then build the evidence and operating practices needed for Type II.
Know where you stand. Plan your next step.
Tell us where you are in your SOC 2 journey. We’ll help you identify the right starting point and the controls to prioritize.
Already working toward an audit? We can help with implementation, Type II preparation and ongoing compliance.